Key highlights
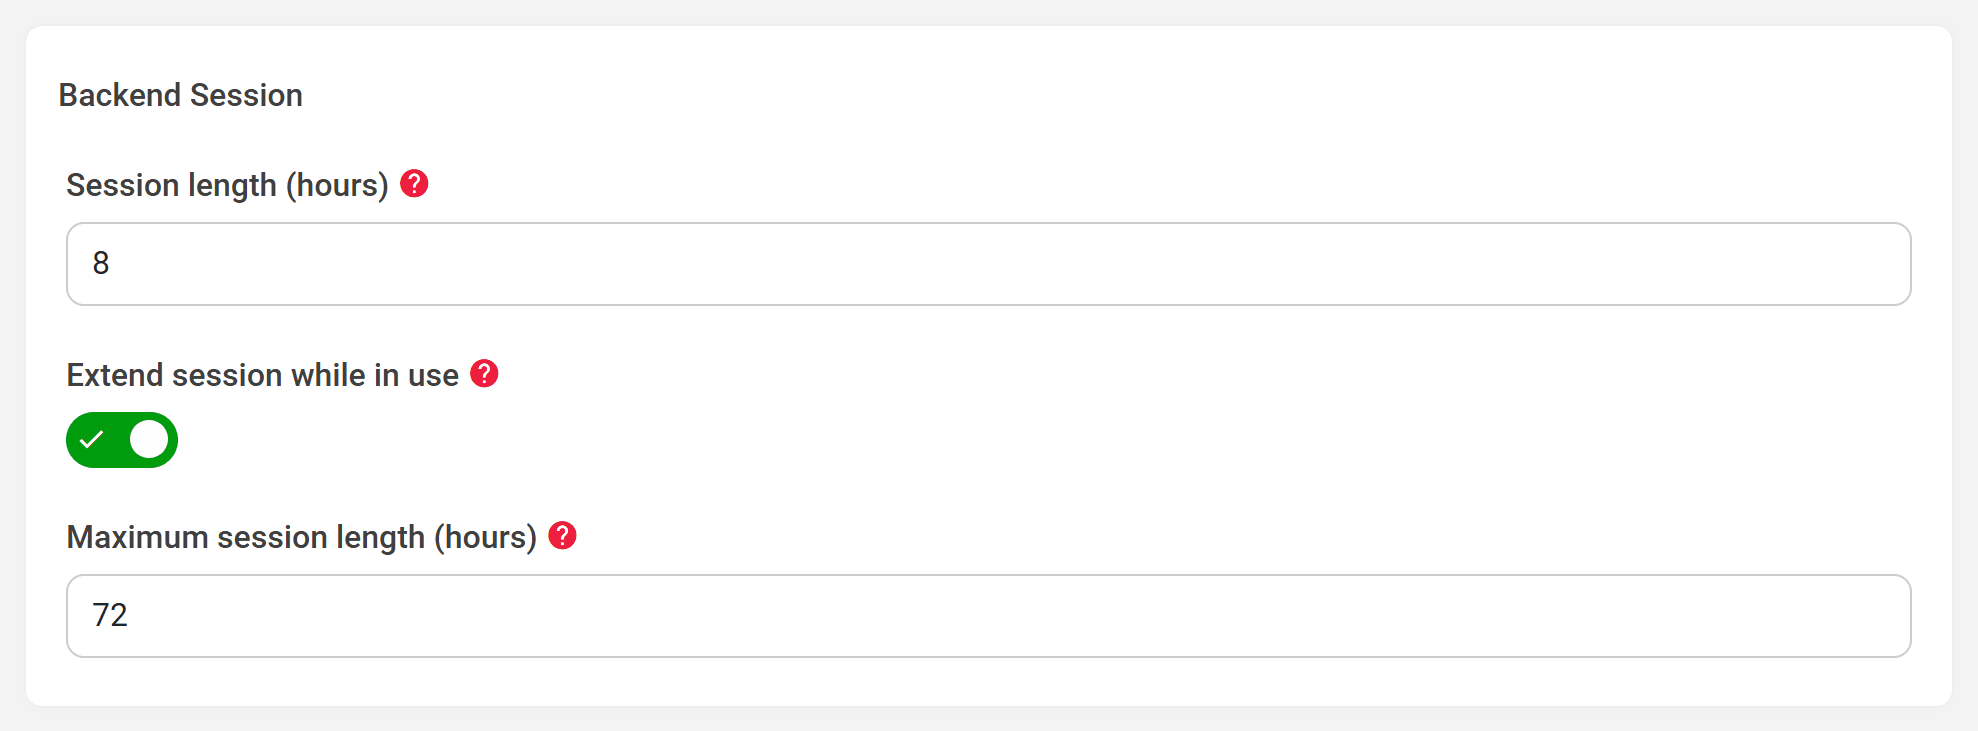
- Admin session length: choose how long an admin session lasts, and keep it open while it is in use.
- Deactivation signs users out: a deactivated user loses every open session at once.
Every Core dna product, release by release, newest first. Each product ships on its own schedule.
Configurable Backend Sessions and Bug Fixes
Administration sessions can be set to last longer and to stay open while they are in use. Deactivating a user now signs them out at once.
How long an admin session lasts is now configurable, in the Backend Session group under Users › OAuth Authentication › Configuration:
Background requests, such as keep-alive checks and edit-lock renewals, do not count as use, so an idle open tab does not keep a session alive.
Deactivating a user now ends their open sessions at once, instead of leaving them signed in until their tokens expire. A deactivated admin with a page still open is signed out on their next request and told that the account is no longer active.
Was this page helpful?
Your answer goes to the docs team.